Indian Institute of Technology Madras
BS Degree Programme · Examination & Study Paper
Modern Application Development I
Validation & access control
Official Paper
Examination Instructions & Guidelines
- Solve on notebook/paper first before checking solutions.
- MCQ: Exactly 1 option is correct. Negative marking applies.
- MSQ: One or more options correct. Select all to score.
- Scientific calculator allowed for all calculations.
- Official answer key is sealed at the end of this sheet.
End Term · 31 Aug 2025 (FN)End Term
- Q1MCQ2 Marks·Choose one option
Consider the following statements and choose the correct option Statement 1: It is mandatory to implement server-side validations and client-side validations. Statement 2: Server-side validations can be implemented using HTML5.
- AStatement 1 is false, while statement 2 is true
- BStatement 1 is true, while statement 2 is false
- CBoth statements are false
- DBoth statements are true
End Term · 13 Apr 2025 (FN)End Term
- Q2MSQ3 Marks·Choose all correct options
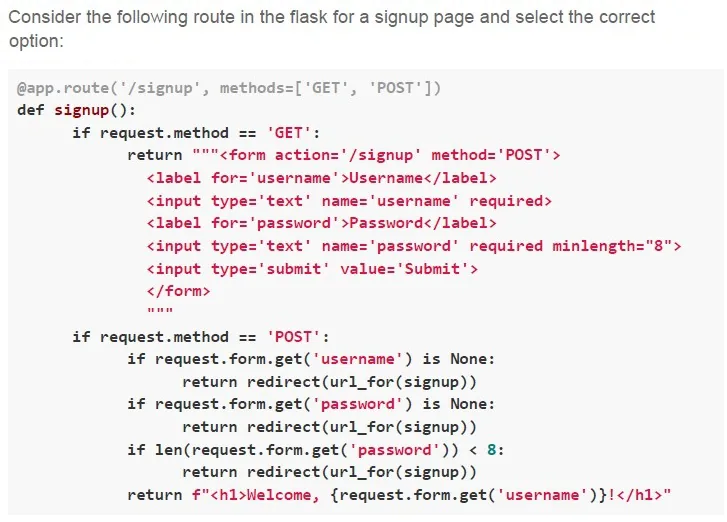
- AThe signup page is dynamically generated.
- BThe signup page uses server-side rendering.
- CThe signup page uses frontend validation.
- DThe signup page uses backend validation.
End Term · 22 Dec 2024 (FN)End Term
- Q3MCQ3 Marks·Choose one option
Which of the following is an example of an application using Attribute-Based Access Control (ABAC)?
- AA system where users are granted access based on their job roles within an organization.
- BA cloud service that grants or restricts access to files based on attributes such as user department, job title, or current location.
- CA file-sharing system where the file owner decides who can access their documents.
- DA system that enforces access based on security classifications and clearance levels.
- Q4MSQ3 Marks·Choose all correct options
Which of the following statements about the Constraint Validation API is/are true?
- AThe Constraint Validation API ensures that form input meets client-side validation rules before submission.
- BThe Constraint Validation API is sufficient to prevent server-side attacks like SQL injection.
- CIt is possible to bypass the Constraint Validation API by directly sending requests to the server.
- DThe Constraint Validation API automatically validates all data on the server side.